Privacy Act statement and background
The authority, purpose and disclosure statement, then background on FISMA, E.O. 14028, the NIST SSDF (SP 800-218) and OMB memoranda M-22-18 and M-23-16, with the conditions that call for self-attestation.
GSA7700
Secure Software Development Attestation
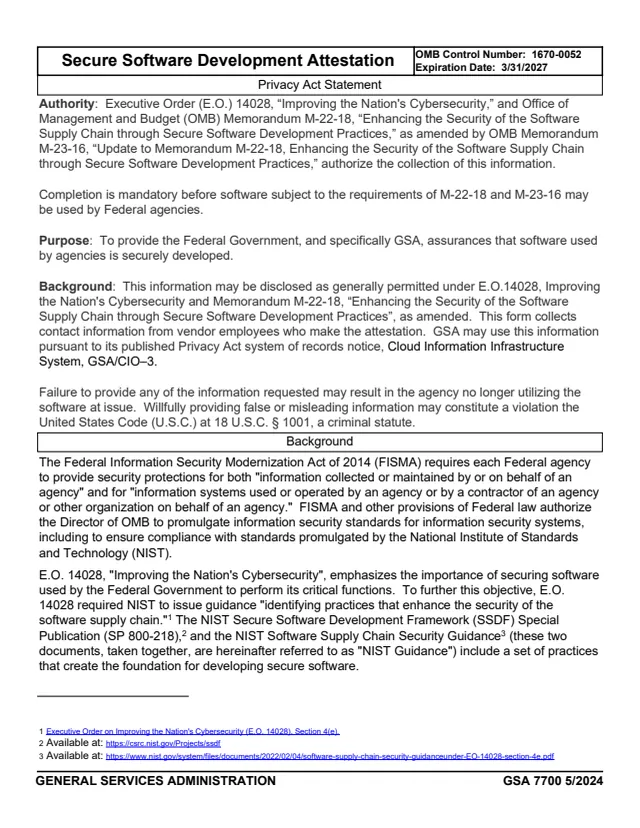
GSA Form 7700, Secure Software Development Attestation, is a General Services Administration form, GSA 7700 5/2024, with OMB Control Number 1670-0052 and an expiration date of 3/31/2027. GSA hosts it in its forms library. Its Privacy Act statement cites Executive Order 14028 and OMB Memorandum M-22-18, as amended by M-23-16, as the authority for the collection.
The form says software providers use it to attest that the software they produce is developed in conformity with specified secure software development practices drawn from the NIST Secure Software Development Framework (SSDF). It says completion is mandatory before software subject to M-22-18 and M-23-16 may be used by Federal agencies, and that its purpose is to give the Federal Government, and specifically GSA, assurances that software used by agencies is securely developed.
Over eight pages it has a Privacy Act statement, background and instructions, Section I on the attestation type and products, Section II on the producer and a contact, Section III with the attestation and signature, a public burden statement and a reference table. You can fill it out free in your browser on this page and download the result without an account.
The authority, purpose and disclosure statement, then background on FISMA, E.O. 14028, the NIST SSDF (SP 800-218) and OMB memoranda M-22-18 and M-23-16, with the conditions that call for self-attestation.
A choice between submitting online at https://softwaresecurity.cisa.gov or saving the PDF under a set naming convention, then instructions on who signs, third-party assessments and a Plan Of Actions and Milestones (POA&M).
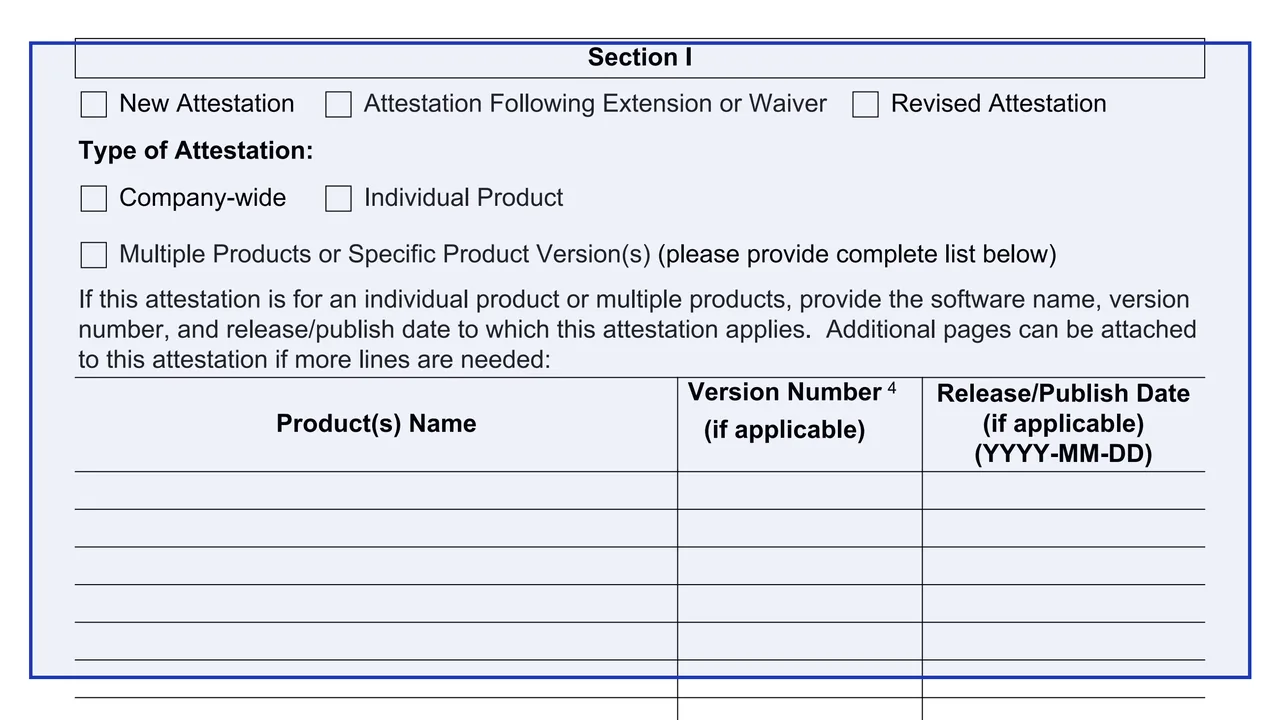
New, following extension or waiver, or revised; company-wide, individual product, or multiple products or specific versions, with a table of product name, version number and release or publish date.
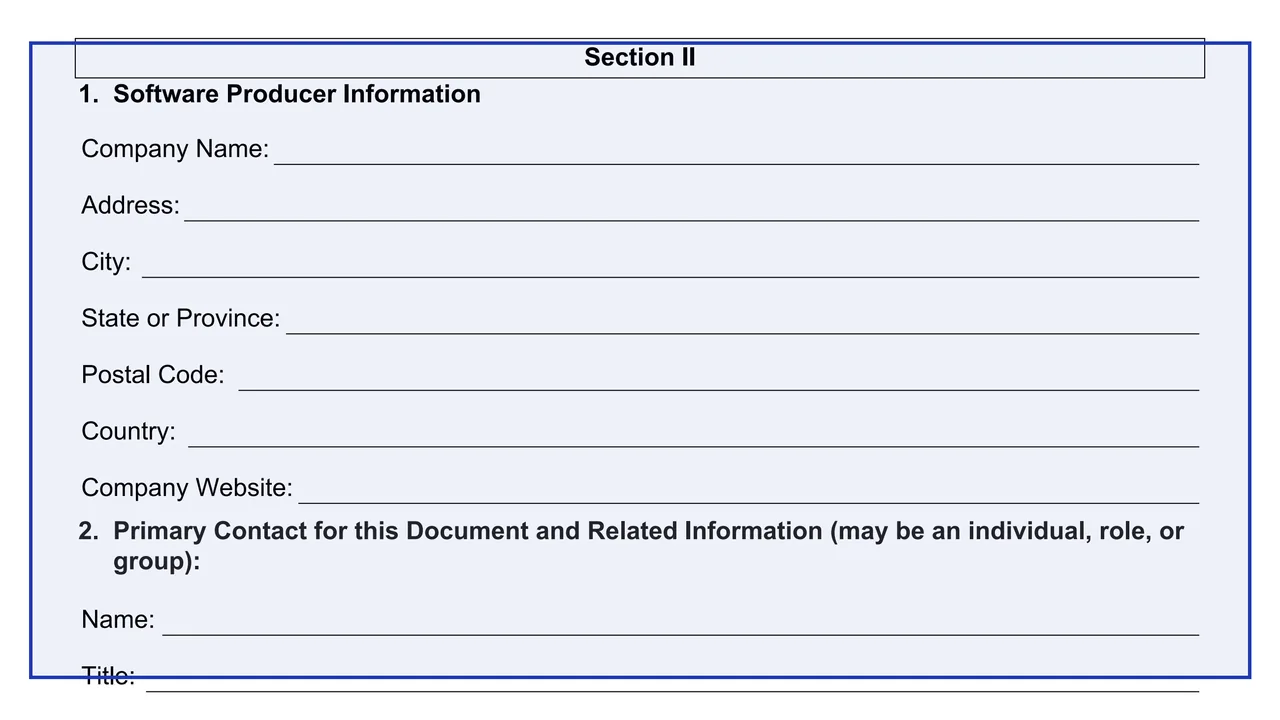
Company name, address, city, state or province, postal code, country and website, then a primary contact's name, title, address, phone number and email address, which may be an alias or distribution list.
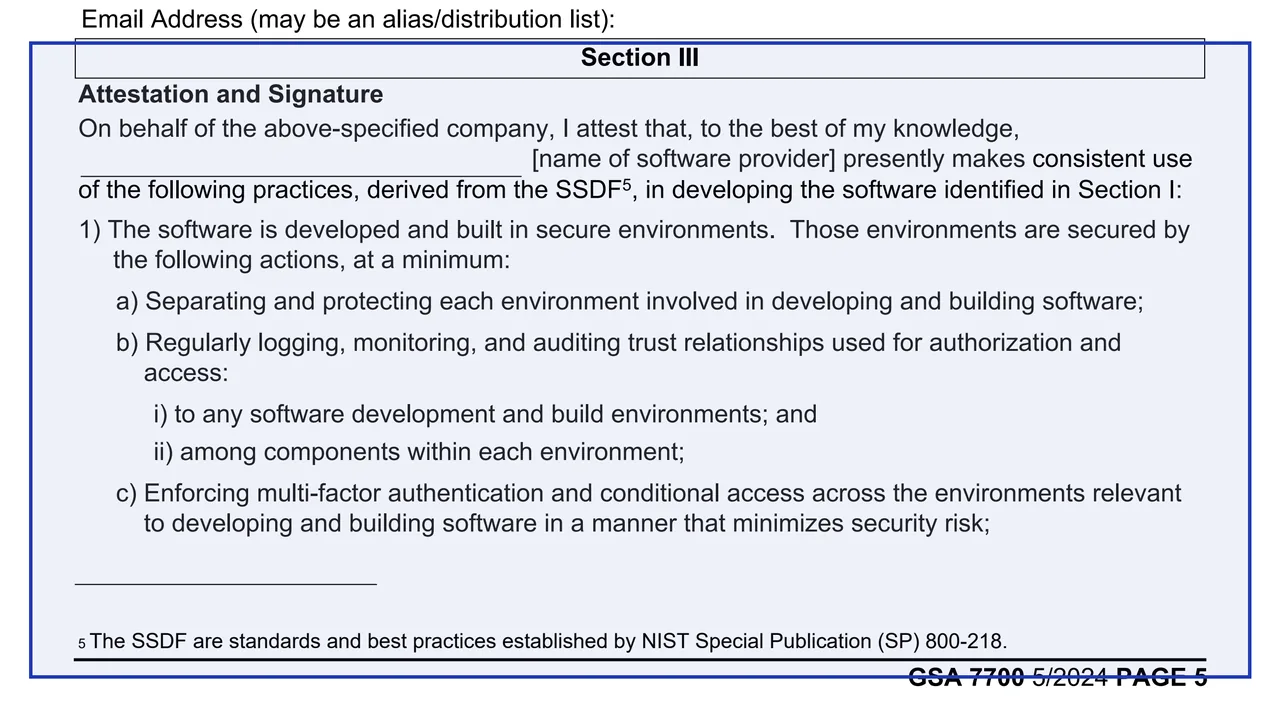
Four numbered practices on secure build environments, trusted source code supply chains, provenance, and automated vulnerability checks with a disclosure program, then the CEO or designee signature, or the 3PAO box and attachments.
The public burden statement and a table mapping each attestation requirement to the related E.O. 14028 subsection and SSDF practices and tasks.
The eight pages hold these parts.
Select online, at https://softwaresecurity.cisa.gov, or save the PDF using the naming convention shown, such as the form's example Acme_SecuritySuite_4.6.2.1_20230124.
Mark the type of attestation and whether it covers the company, one product or multiple products or versions, and list each product name, version number and release date as YYYY-MM-DD. Additional pages can be attached.
Enter the software producer information and the primary contact for the document and related information.
Enter the name of the software provider in the attestation, then the CEO or designee signs and gives the date as YYYY-MM-DD, name and title.
Check the box stating that a certified FedRAMP 3PAO or other approved 3PAO has evaluated conformance, and list attachments as [Artifact/Addendum Title]: [Artifact/Addendum Description].
When not submitting online, the form says to send the completed PDF form to GSA by email at [email protected].
You get the real form, filled in a browser tab, with nothing standing between you and the finished PDF.
Online at https://softwaresecurity.cisa.gov, or the completed PDF by email to [email protected]. The CISA email in the burden statement, [email protected], is for comments on the burden estimate.
The public reporting burden is estimated at 3 hours and 20 minutes per response, including time for reviewing instructions, searching data sources, gathering and maintaining the data, and completing and reviewing the collection.
OMB Control Number 1670-0052, expiration date 3/31/2027.
A footnote says attestations are binding for future versions of the named software product unless and until the producer notifies the agencies it submitted the form to that its development practices no longer conform.
The Privacy Act statement says willfully providing false or misleading information may constitute a violation of 18 U.S.C. § 1001, a criminal statute.
The background and instructions describe who completes, signs and receives it.
No tool matches that search.
It is printed as a General Services Administration form, GSA 7700 5/2024, with OMB Control Number 1670-0052. Its burden statement directs comments to the U.S. Department of Homeland Security (DHS), Cybersecurity and Infrastructure Security Agency (CISA).
The form lists software developed after September 14, 2022; software developed before then but modified by major version changes after it; and software whose producer delivers continuous changes to the code, as with software-as-a-service.
Software developed by Federal agencies, open source software freely and directly obtained by a Federal agency, third-party open source and proprietary components incorporated into the end product, and software that is freely obtained and publicly available.
The form says the CEO of the software producer or their designee, who must be an employee of the software producer and have the authority to bind the corporation.
Yes, the form says a producer may submit an assessment by a FedRAMP-certified 3PAO or one approved in writing by an appropriate agency official, check the box in Section III and attach it. The producer need not sign in that case.
The form says an agency may still decide to use the software if the producer identifies the practices it cannot attest to, documents practices that mitigate the risks and submits a Plan Of Actions and Milestones (POA&M) to the agency.
The burden statement estimates 3 hours and 20 minutes per response, including time for reviewing instructions and gathering the data.